Learn
Learn
Plain explanations of the threats SphereTI monitors — what each one is, how it reaches an organisation, and what actually detects it.
Showing 10–18 of 18 articles
Vulnerability intelligence
Why CVSS Scores Don't Tell You What to Patch
NIST stopped scoring every CVE in April 2026. What that tells you about severity-based triage.
Read
Dark-Web
What Is an Initial Access Broker?
The intermediaries who turn a stolen password on a home laptop into a ransomware incident.
Read
Brand protection
What Is Typosquatting?
Why the domain that impersonates you passes every email authentication check you have.
Read
Credential theft
What Is Session Cookie Theft?
The theft that survives a password reset, and why revocation is a separate action most teams skip.
Read
Credential exposure
What Is a Combolist?
What aggregated credential lists reveal, what they cannot prove, and how to respond to exposed accounts.
Read
Credential theft
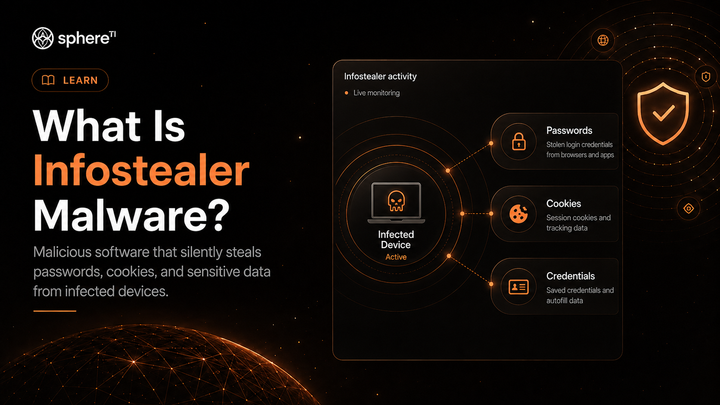
What Is Infostealer Malware?
The commodity malware behind most credential exposure, examined from delivery through to monetization.
Read
Credential theft
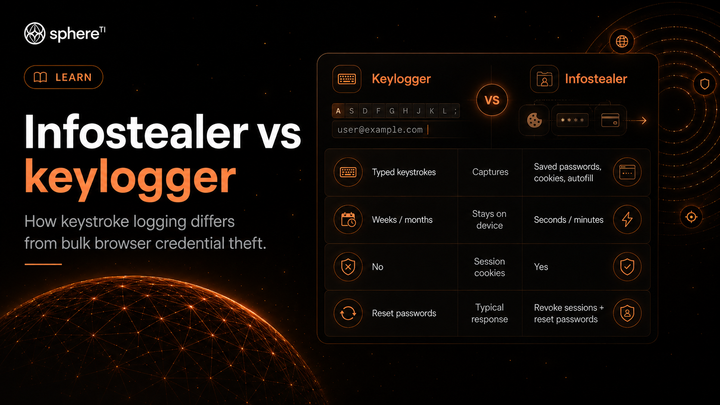
Infostealer vs Keylogger: What's the Difference?
The two main ways credentials get stolen, and why only one of them survives a password reset.
Read
Credential exposure
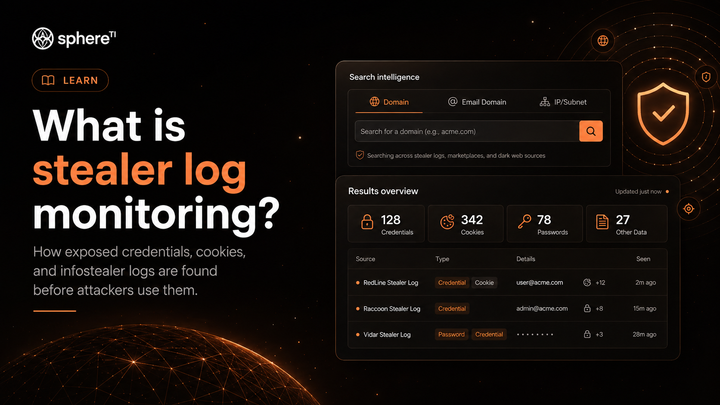
What Is Stealer Log Monitoring?
What infostealer malware takes, why breach checks miss it, and how monitoring closes the gap.
Read
Cyber decoys
What Are Cyber Decoys?
Fake assets that nothing legitimate should ever touch — and what it means when something does.
Read